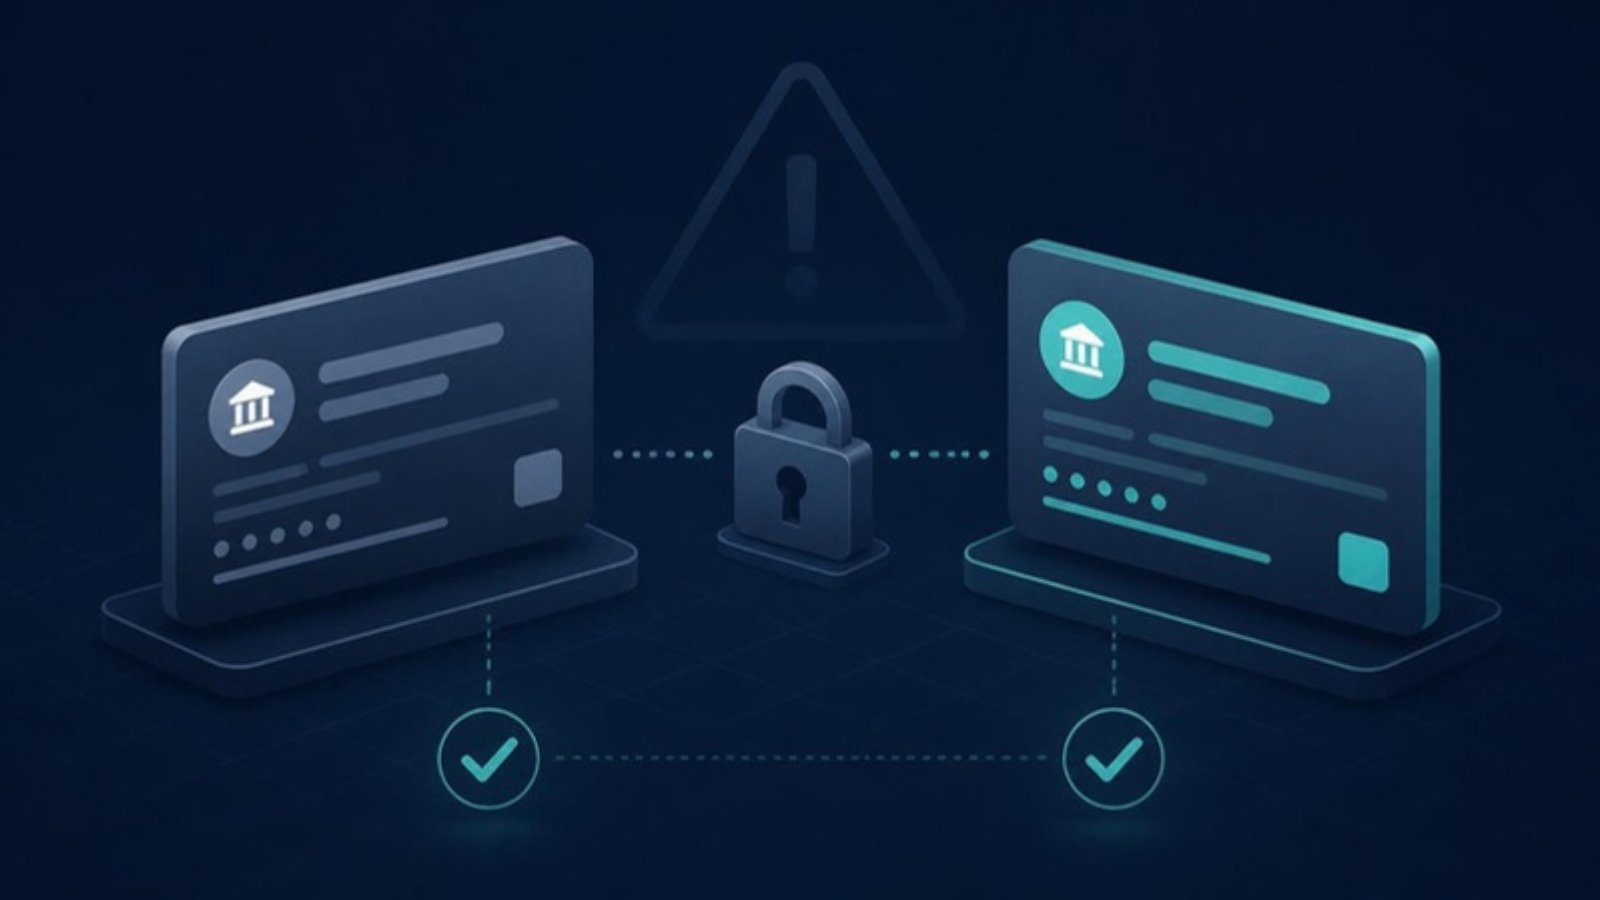
Changing a vendor's IBAN is one of the most common fraud scenarios in accounting: a fake email announcing new bank details, an edit made in the ERP, and the next transfer goes to a fraudulent account. This article explains why control cannot rest on one person or one system, and how dual validation between Sage Intacct and Arkaio reduces the risk.
Why IBAN changes are a weak point
In a traditional setup, an authorized user edits the vendor record, sometimes on the strength of a simple email. The next payment uses the new details with no further check. The consequences are serious: funds that are hard to recover, an internal investigation, a strained supplier relationship. The risk comes from external fraud as much as from keying errors.
A typical scenario
An accountant receives an email that appears to come from a regular supplier: "We have changed banks, please use this new IBAN for the open invoice." They update the vendor record in Sage Intacct. Without any further control, the next payment batch goes to the fraudster's account. With dual validation, the change stays pending in Arkaio: a second user must approve it before the new IBAN can be used for any payment.
The principle: one change, two validations
- Change made in Sage Intacct: it generates an approval request in Arkaio.
- Change made in Arkaio: Sage Intacct is only updated once the change has been accepted.
- No self-approval: the person who made a change cannot approve it.
- Old and new IBAN side by side: the approver sees exactly what is changing.
A compromised account or a single entry is therefore not enough to redirect a payment. This complements the separation of duties described in our article on distributed electronic signature (VEU).
Red flags for the approver
- a bank or country that does not match the vendor's usual details;
- an urgent request, just before a due date or a payment run;
- a sender address that mimics the vendor's usual domain;
- a request for discretion or to bypass the normal procedure.
In these cases, calling the vendor back on a number you already have, not the one in the email, remains the right reflex.
Additional controls before payment
- IBAN and BIC verification before payment is prepared: a non-compliant invoice cannot be selected.
- Frozen amounts as soon as the user enters them.
- Abnormal behavior detection through machine learning (unusual activity, IP address changes): the affected payments are blocked.
- Configurable rights and workflow: approving or cancelling a payment depends on the roles defined in Arkaio.
Once the batch is sent, pain.002 status tracking flags any rejection by the bank.
What about Verification of Payee (VoP)?
Since 9 October 2025, banks in the euro area must check, before a transfer, that the payee's name matches the IBAN (EU Regulation 2024/886). It is a useful safety net on the bank side, but it only comes into play at the moment of payment and does not cover every flow, especially outside the euro area. Upstream internal control remains necessary.
Use cases
- SMEs: dual validation adds a second pair of eyes without heavy procedures.
- Mid-market and multi-entity groups: approvals follow the roles of each entity.
- Accounting firms: changes are traced per client file, as covered in centralizing multi-client payments.
Limits and audit trail
Dual validation protects the payment flow, not the origin of the request: an approver can also be misled by a convincing email. On the other hand, every action is logged (who changed what, who approved, and when), and the evidence is available in Arkaio for an auditor, CFO or CISO. Our other safeguards are described in the security section.
Key takeaways
Securing IBANs should not slow payments down. With Intacct/Arkaio dual validation, control is built into the flow: legitimate changes follow a clear approval path, and fraudulent attempts stop before the bank.